Who We Are
Global Secure Solutions is a cybersecurity advisory firm focused on regulatory cyber defensibility. We work with financial institutions, critical infrastructure operators, and regulated organisations across Ghana and West Africa.
Our practice is built on a single observation: in high-scrutiny environments, the organisations that navigate regulatory examination are not those with the most sophisticated technology, but those who can demonstrate, clearly and consistently, that their controls are real, proportionate, and operating as intended.
We do not sell tools or run generic training programmes. We structure cybersecurity postures so they can be defended under examination, during incidents, and throughout regulatory cycles.
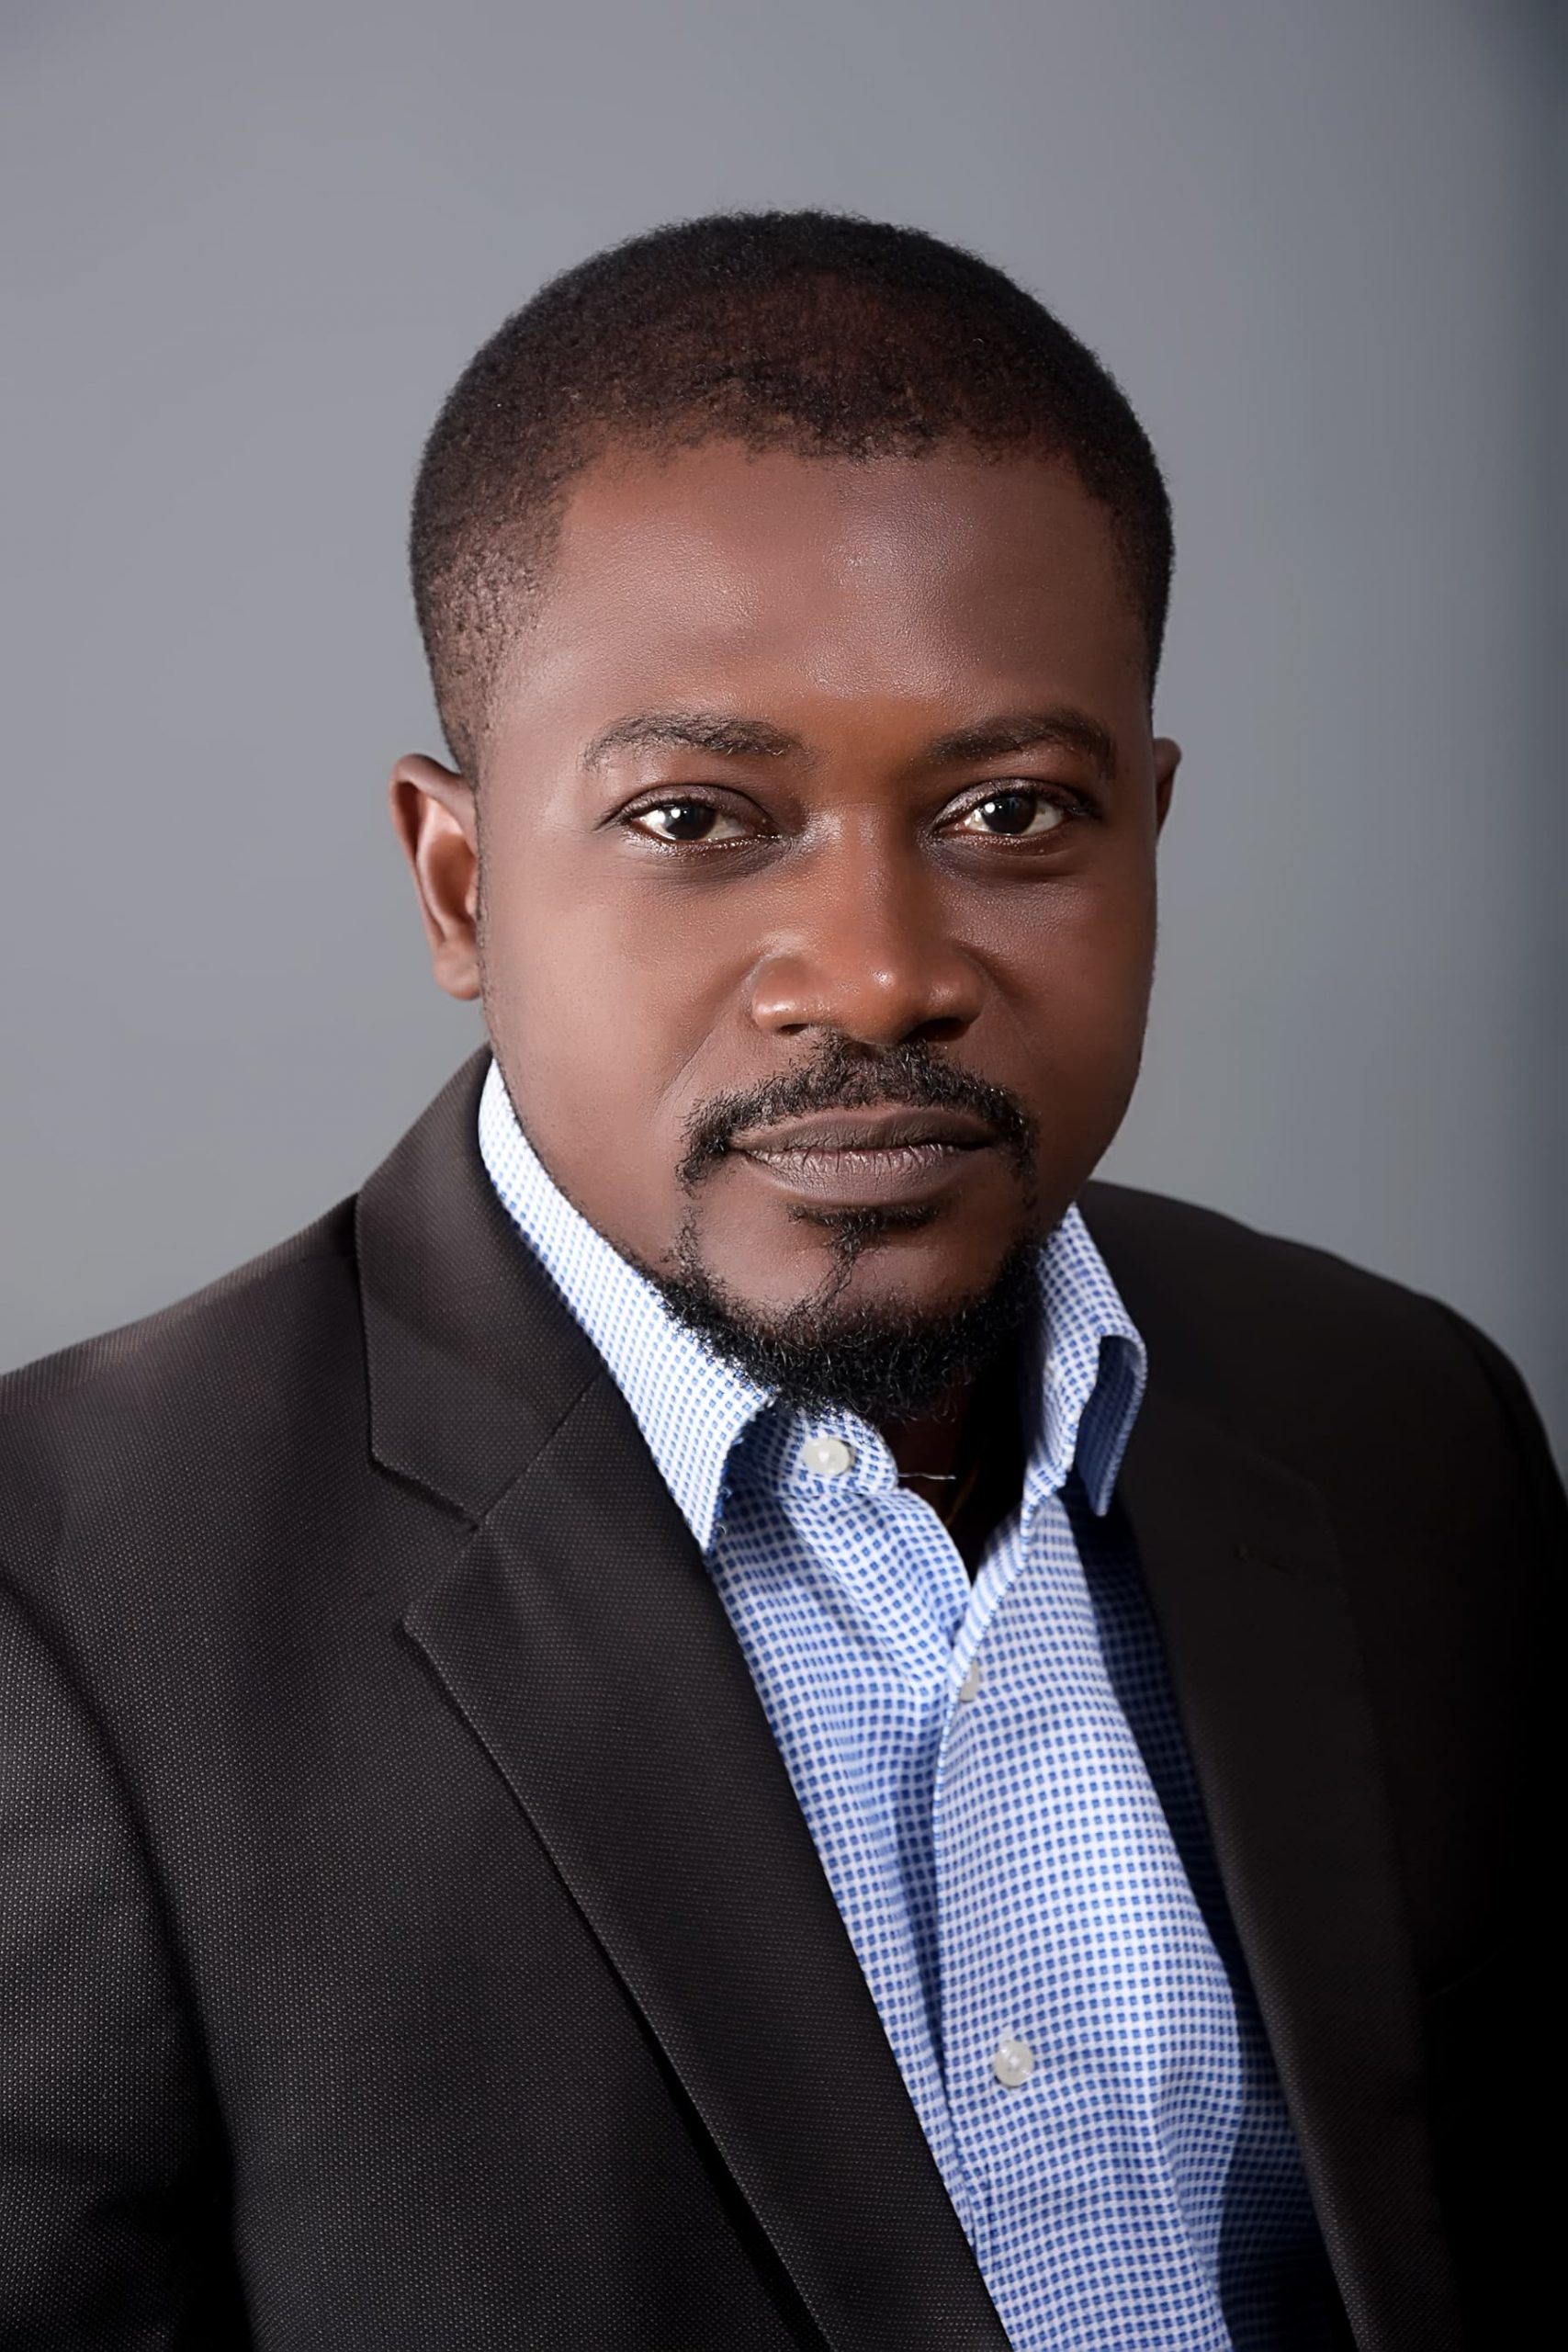
Edem Glymin
Edem Glymin is a cybersecurity, technology-risk and regulatory-assurance leader with more than 15 years of experience spanning financial services, critical infrastructure, consulting and executive leadership. As Founder and CEO of Global Secure Solutions, he has led and advised regulated organisations on cybersecurity assurance, resilience, governance and emerging ICS/OT risk, with a strong emphasis on translating complex regulatory and technical requirements into defensible executive action. His approach to Regulatory Cyber Defensibility is grounded in a simple principle: effective cyber governance must go beyond policy and nominal compliance. Organisations should be able to demonstrate, with credible evidence, how regulatory obligations are translated into control expectations, how those controls operate in practice, where material exposure remains, and how that position can withstand regulatory, audit, executive and board scrutiny.
- Assess cybersecurity postures against regulatory defensibility standards
- Structure control frameworks to meet examination-level scrutiny
- Support financial institutions through SWIFT CSP attestation
- Respond to incidents in a manner that protects regulatory position
- Maintain defensibility posture through continuous oversight services